*THIS IS A SERIES! BE SURE TO START AT PART 1! [Click Here]*
While people are horrified of what Flock is doing because Flock is a physical object that can be seen, what we can’t see is just as bad, perhaps worse.
For all of the people who keep saying they don’t care if strangers are harvesting their data because they have done nothing wrong, let me tell you what this next company does, and you tell me if anything on this list crosses your line…
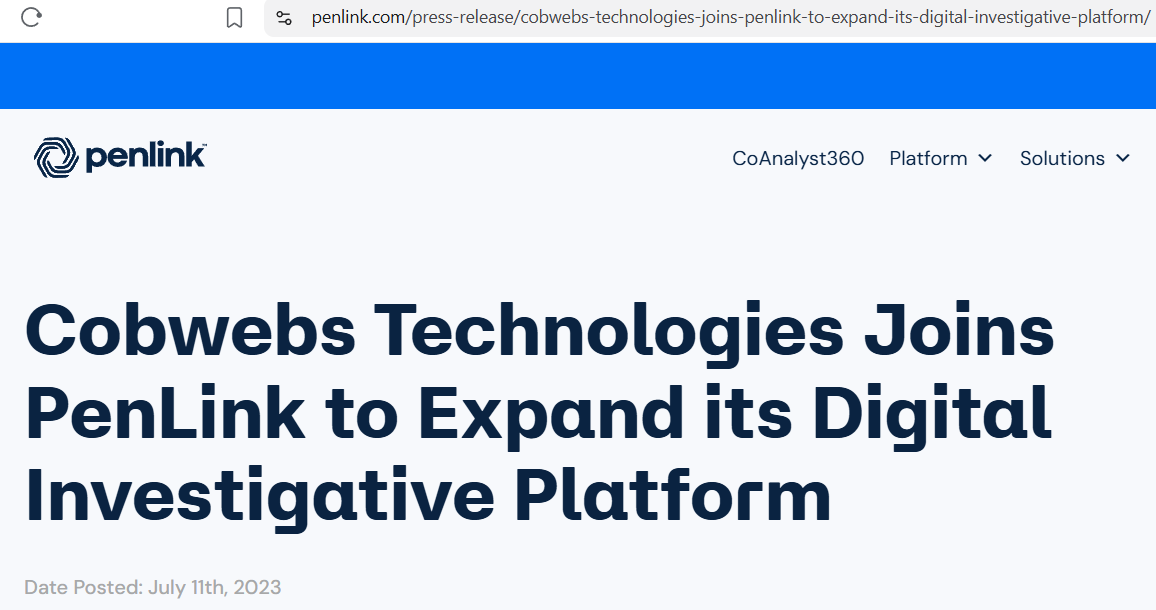
PenLink is a software company that develops high-end commercial communications, surveillance, data collection, and analysis products for law enforcement. “Tell me more,” you say. In July 2023, PenLink merged with Israeli surveillance contractor Cobwebs Technologies. Cobwebs was founded in 2015 by former members of Israeli special forces and intelligence units. Do you guys remember the Pegasus spyware scandal? In the scandal, the NSO Group, an Israeli cyber-arms company, sold its cutting-edge surveillance software to governments. While the plan was supposed to be to use this tech to catch bad guys, that is not what happened. Governments instead used it to target journalists, human rights activists, politicians, and dissidents. Fellow journalists claim the same company that developed Pegasus is the same company that developed Cobwebs, so we are talking about some major technology here.
The three founders of Cobwebs Technologies have since taken over key executive roles at Penlink, so Penlink is a mashup of the two entities.
Through their technology, Cobwebs provides “web intelligence solutions,” which allow users of the tech to, quote, “pinpoint web relations, criminal activities, and terrorist threats with a click of a button.” According to Cobwebs, they work with clients from all over the world.
There is no better way to learn about a company than by looking at their products, and thanks to Citizen Lab’s outstanding research, we can do just that. Penlink / Cobwebs developed the following products:
Tangles, a web platform that scrapes data from the open web, deep web, and dark web. This allows for the tracking of mobile devices within a user-designated area (geofencing.) According to leaked training manuals, government and commercial customers can search for keywords and personal identifiers, which include name, email address, phone number, and usernames. Once the search is run, the government or commercial customer can then identify online accounts and analyze what they post, view their interactions, relationships, activities, likes, dislikes, and event attendances. Yes, these bastards know what events you attended in your leisure time. Additionally, users can monitor and profile individuals, create “target cards” and receive alerts when a target does something; analyze geolocation information extracted from posts and photos; and perform network analyses.
Now here’s why this is so important: Some of the data sources that we know Tangles is pulling data from include web forums, blogs, text storage sites (aka “pastebins”), Facebook, Facebook Marketplace, Instagram, Twitter/X, YouTube, LinkedIn, SnapChat, TikTok, Reddit, VK, Parler, Gab, and even the dating platform Tinder—but that’s not all. They also get your conversations from Telegram! Yes, they get your Telegram communications! Which is quite interesting because the government claims they can't stop the crime running amok on the site because it's encrypted. Clearly that’s not true.
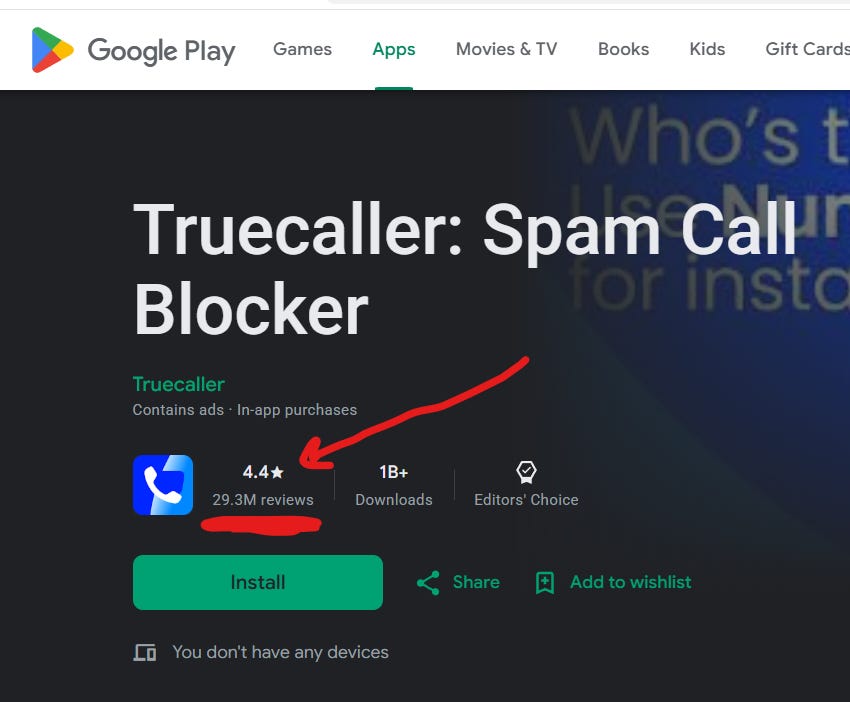
Additional data is pulled from Truecaller, which is a caller ID smartphone app! This cell phone app has almost 30 million reviews, just in the Google Play Store. That means no less than 30 million people are having their call information harvested for Tangles, and I guarantee not a single person knows this.
We will circle back to cell phone apps later in this publication.
Those are just a few of the apps Citizen Labs was able to confirm Tangles is using for data gathering. I guarantee there are dozens, if not hundreds, more. So, anyone using Tangles can type nothing more than your phone number or email address into the database, and it will spit out a biography of your life, including your Telegram conversations, your caller ID records, what you are buying and selling on Facebook, and Lord only knows what else.
Who are Tangle’s clients? Who truly knows the extent of it, but we do know the US Department of Homeland Security (DHS) enjoys the software because it allows them to “compile dossiers” on protesters and other citizens that they don’t approve of. Although all of this is done under the guise of keeping you and me safe, DHS was caught red-handed engaging in social engineering, meaning the psychological manipulation of people to get them to perform actions or divulge confidential information. Obviously, DHS denies such claims.
Additional US-based clients include ICE, the U.S. military, Texas Department of Public Safety, DHS West Virginia, NYC district attorneys, and several police departments in Los Angeles, Dallas, Baltimore, Tucson, and Durham, as well as those in smaller cities and counties like the City of Elk Grove and Pinal County.
I should mention Tangles offers its users a convenient mobile app because you never know when you will need to spy on someone while on the go, and it too was developed by Israel.
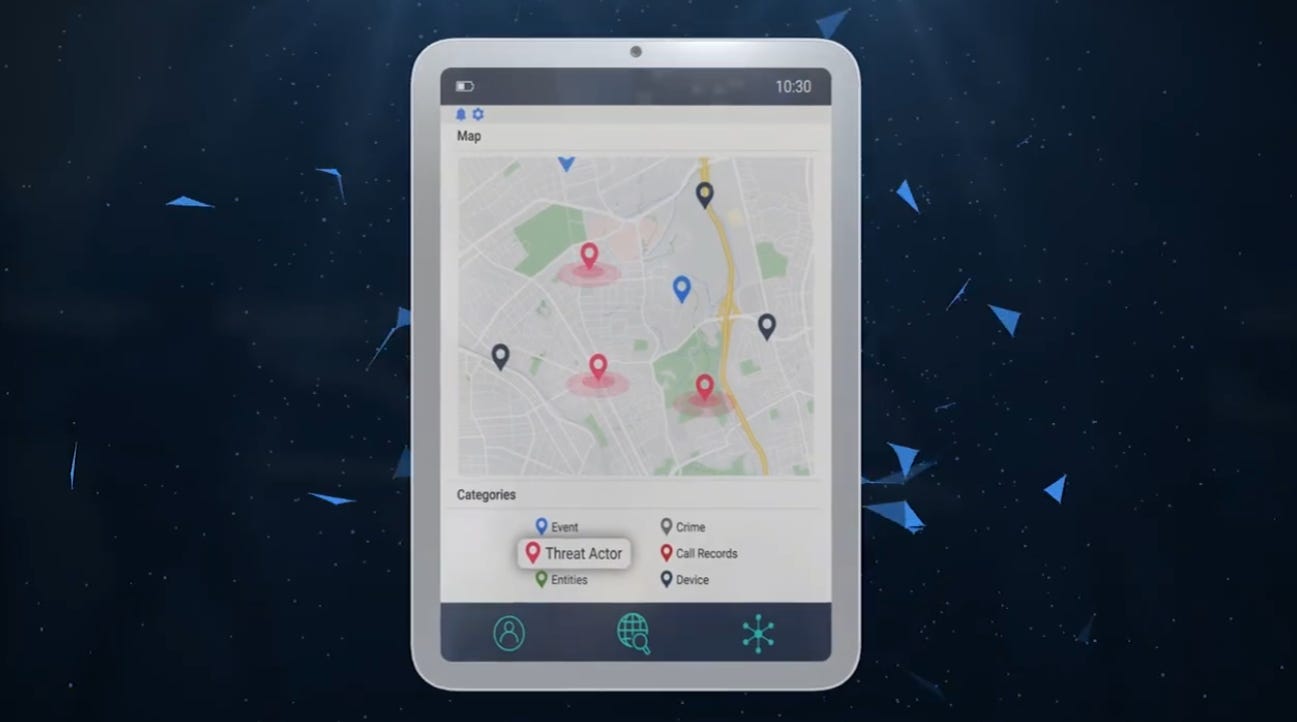
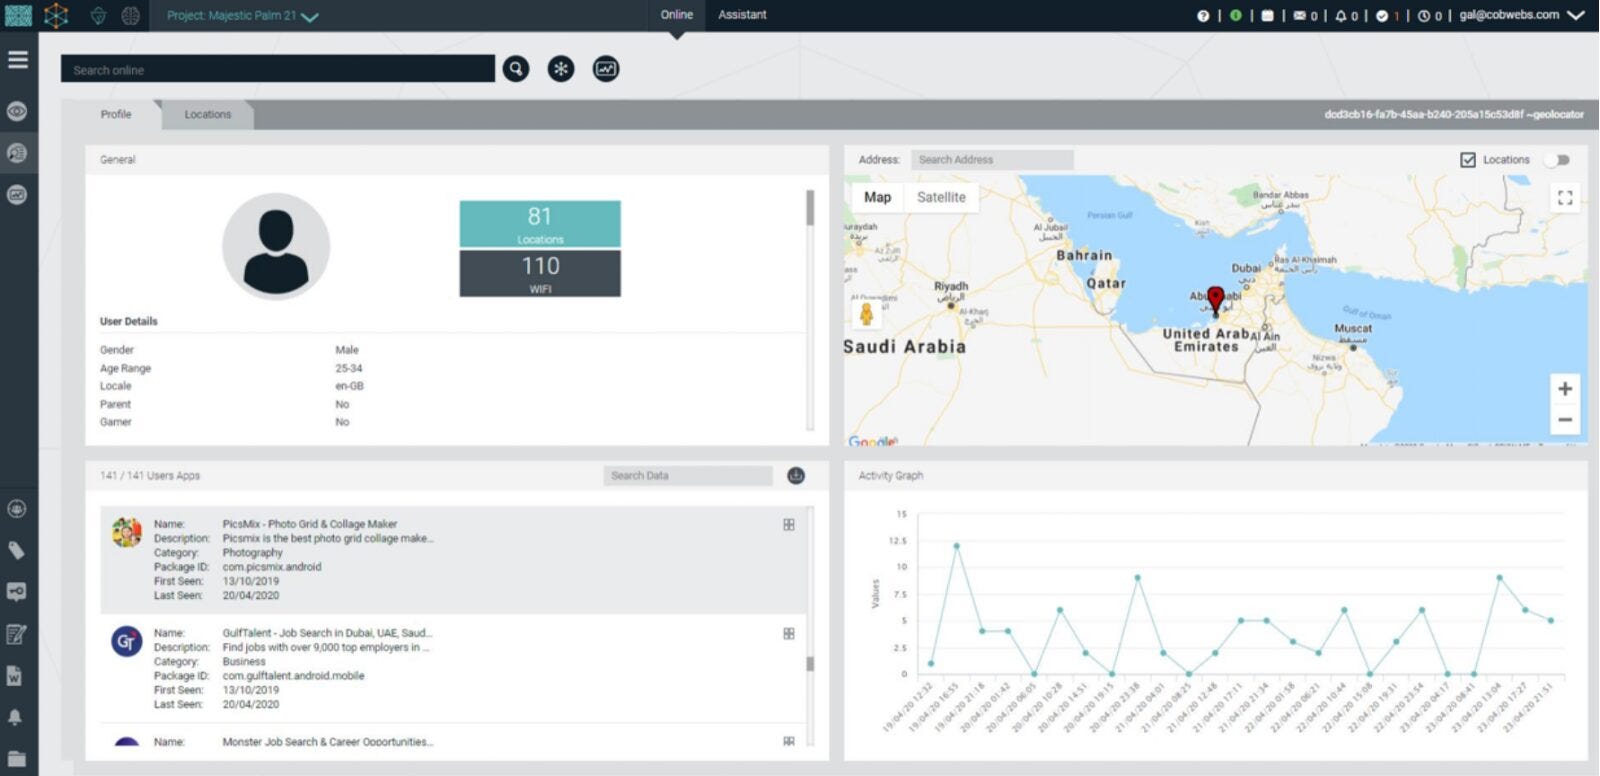
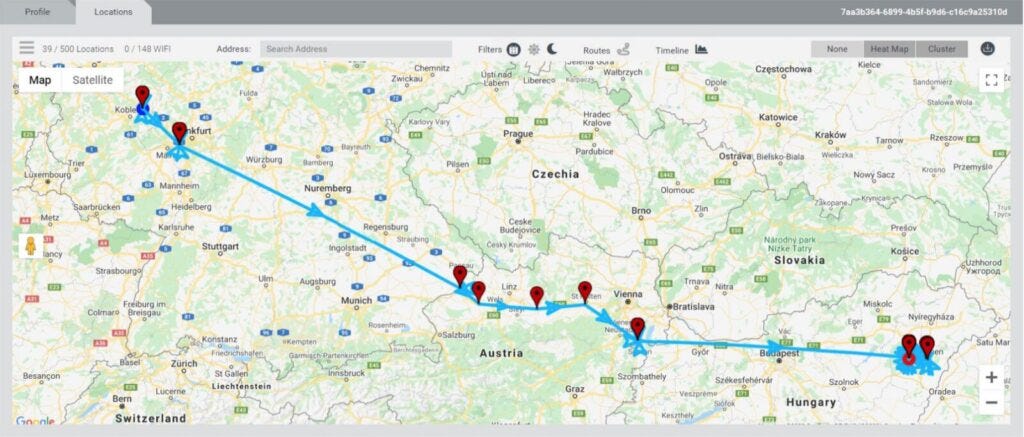
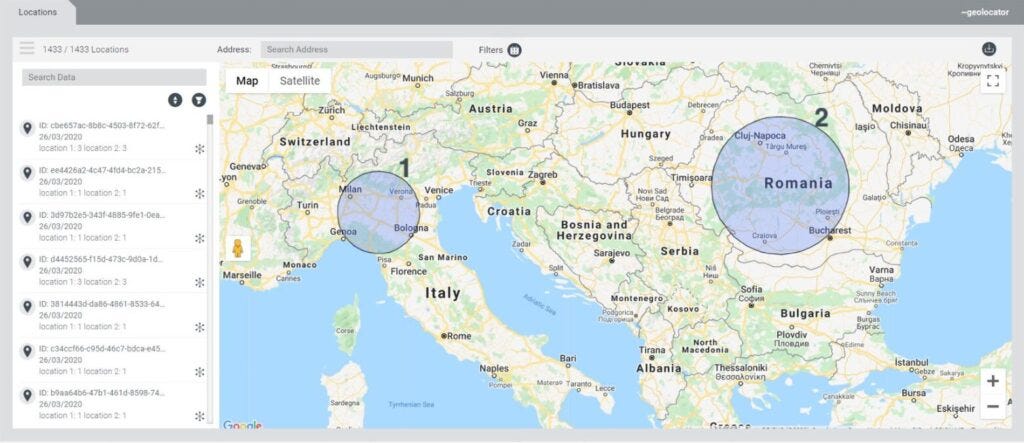
The next piece of technology that Cobwebs developed is called Webloc, which is described by journalists as an “ad-based geolocation surveillance system reported to have processed data associated with up to 500 million mobile devices.” Webloc relies on data purchased from mobile apps and digital advertising. This includes GPS, Wi-Fi location data, IP addresses, and more. (We will cover this thoroughly in the next part of this publication).
Webloc’s technology (also developed by Israel) focuses on “large-scale tracking of location patterns, movement analysis, and inference of behavioral profiles.” This program is Google Maps on steroids. Check out these screenshots from it.
Tangles and Webloc are not the only programs being solicited by Cobwebs and Penlink. Lynx is another program that provides investigators with the capability to use social media platforms with fake identities and fake accounts. These fake accounts not only work on social media, but they also work in forums and even via email. All of this is run through a global proxy server infrastructure to mask the identity and location of the user.
Lynx does a lot more than offer users the opportunity to catfish and spy on people anonymously; the program itself also manages avatars and offers virtual agents, so it appears the fake accounts run themselves.
Clients include the Los Angeles Police Department as well as US federal agencies, including DHS and the Internal Revenue Service (IRS). Yeah, folks, the IRS purchased deception software that makes and runs fake accounts.
Another one of Cobwebs’ programs is Trapdoor, which Cobwebs promoted as an “active web intelligence” solution, but because it is so secretive, little is known about it or reported on it. Citizen Labs was able to obtain a technical specifications document that flat out refers to the program as a “social engineering platform.” While Lynx focuses on tricking people on social media as well as other methods of communication, Trapdoor is designed to create fake websites in a matter of seconds or minutes. These sites that Trapdoor creates are untraceable, professional-looking bogus websites, complete with a URL. It can then generate links, which, if clicked, will infect the victim’s device. Yeah, this program can throw together websites. This got me thinking about those fucky sites with the fucky font and fucky colors previously discussed. Were these instantly generated by a computer program? If so, that would explain a lot.
Additionally, Trapdoor sends targets phishing links. Phishing links are links that look like they are to one thing but are actually to something else. For example, you receive an email claiming it is from your bank that says you overdrafted your account. Although the link looks like it is from your bank, it is not. Unless you look closely, you won’t notice the name of the bank is spelled wrong in the URL because the link is fake. But, unlike traditional phishing links, Trapdoor has the ability to disguise a link as any website, so in this case, it will say the actual URL of your bank, and there will be no way to distinguish that it is a fake link.
Through the Trapdoor program, when the victim clicks on the link, malware will be installed onto their device. By definition, malware is “any software intentionally designed to cause disruption or destruction to a computer, server, client, or computer network; leak private information; gain unauthorized access to information or systems; deprive access to information; or interfere with the user's computer security and privacy without their knowledge.”
Once the link is clicked, Trapdoor allows its customers to access a device’s camera and microphone, remotely open hidden tabs in the victim’s web browser, and deliver “payloads” to them. Additionally, information about the phone itself can be viewed, such as battery level, IP address, browser type, language, version and plugins, operating system and version, device type, CPU and GPU information, screen resolution, ISP information, estimated geolocation, user inputs, timezone, and even charging status. If available, it also provides “social media details” and “location network details.” Worse, the malware installs a keylogger, which means every key you type is logged—every text message, every email, every password to every website; it is all recorded as you type it.
Once the malware is installed, it begins to run, which includes performing actions on the target’s browser. It can close browser windows and open hidden tabs, all the while extracting media stored on your phone or computer.
Penlink claims they no longer sell Trapdoor, yet Citizen Labs was able to identify potential Trapdoor servers located in Kenya, Indonesia, Singapore, Hong Kong, the UAE, and Japan.
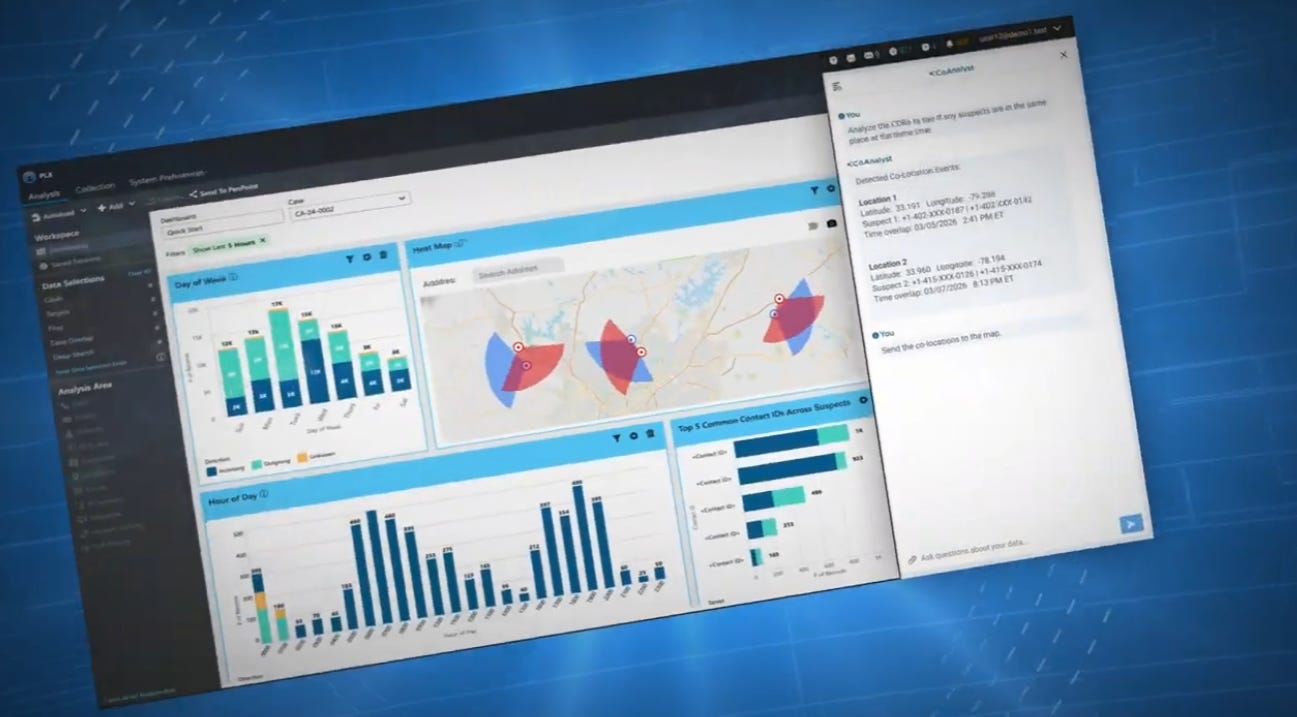
Next up is PLX, which, according to a commercial shown on Penlink’s YouTube channel, allows “investigators to uncover hidden connections, relationships, and patterns of activity between points of interest” (which means you and I). PLX helps to retrieve, organize, and analyze call records, search histories, login data, and other information from AT&T, Verizon, T-Mobile, Comcast, Google, Facebook, and other companies.
In 2022, Penlink had contracts worth $20 million a year with US federal agencies, including ICE, the FBI, and the DEA, and many more with local and state police.
Then there’s WebEye. A leaked document described WebEye as a system for “investigations of web pages and browser session extraction.” This program is also secretive, so there isn’t much to learn about it without booking a consultation through Penlink.
Pen-Link 8 and LINCOLN2 are two more comprehensive electronic surveillance systems for intercepting and monitoring various forms of communication, including wireline, wireless, satellite, VoIP, and 3G networks. Yes, wiretapping. It’s literally wiretapping. They also own PenProxy and Xnet. I have not been able to dig up anything on these two programs.
QUADREAM, I-OTT & FALKOR
Cobwebs is linked to Quadream, an Israeli surveillance technology company that was founded in 2014 by a group including two former NSO Group employees (the Pegasus spyware people). Quadream is known for its spyware marketed under the name “Reign,” which, like Pegasus, reportedly utilizes zero-click exploits to hack into target devices. A zero-click exploit is a sophisticated cyberattack that compromises a device or system without requiring any interaction from the user.
Once this spyware is installed, the individual running it has full control of the device.
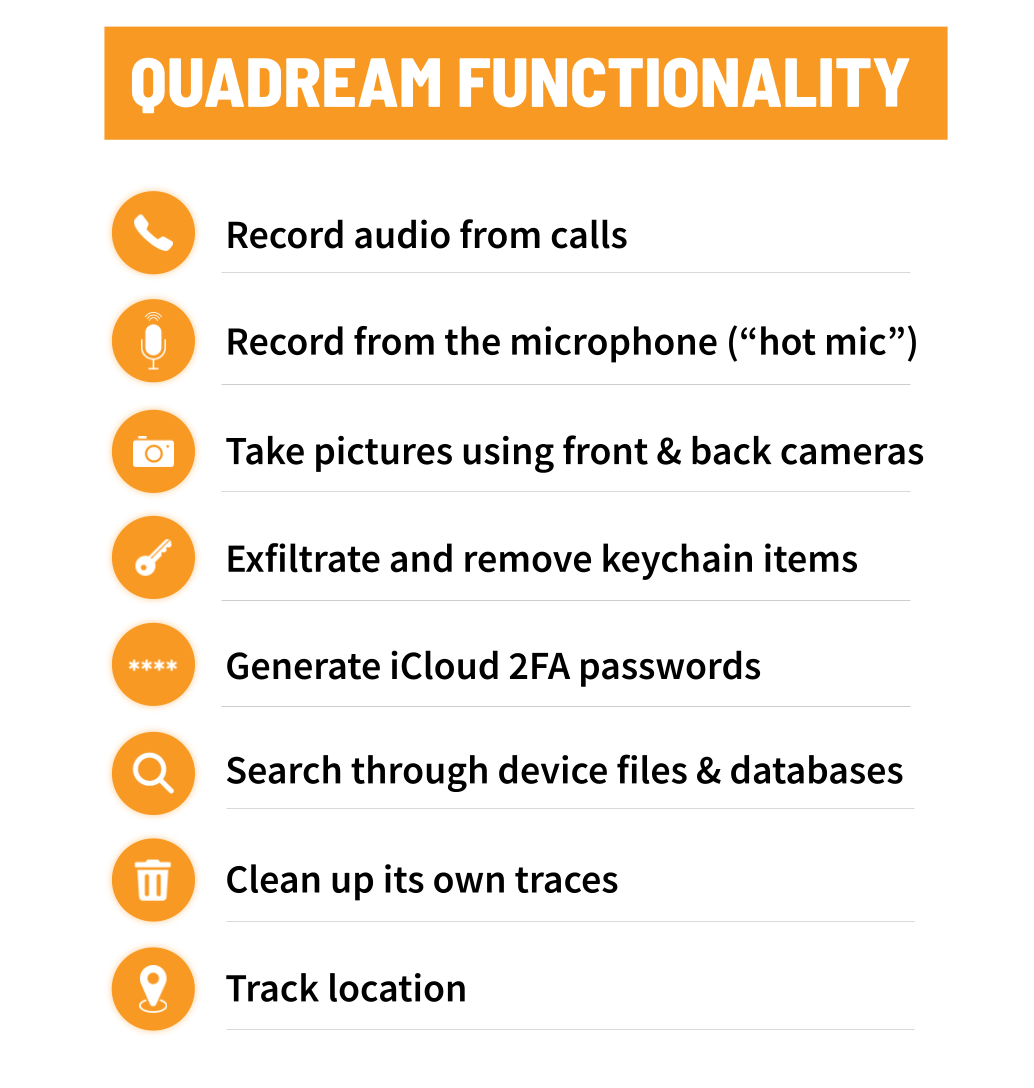
The Citizen Lab discovered that Quadream’s spyware was used to target civil society, journalists, and political opposition figures in North America, Central Asia, Southeast Asia, Europe, and the Middle East.
I-OTT
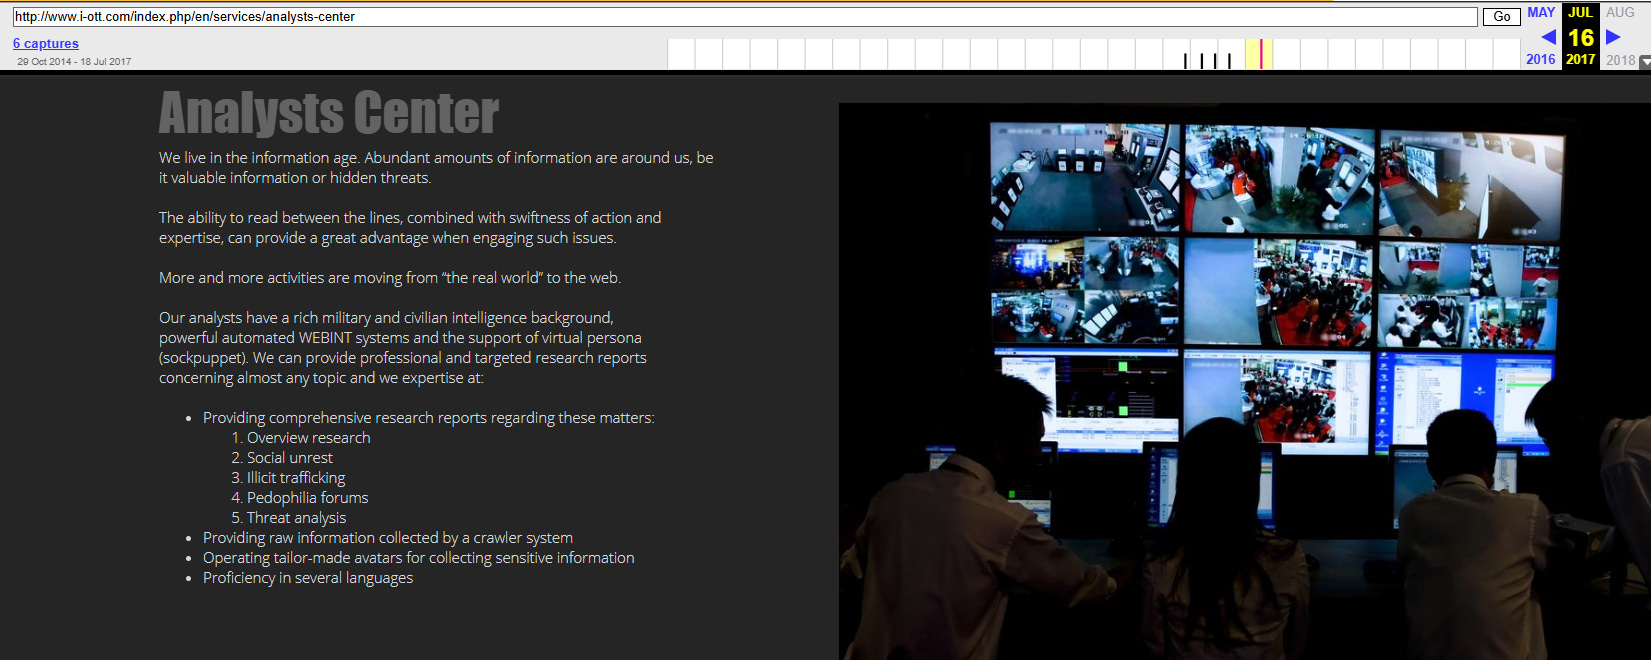
According to company registration documents from Israel, the investors in Cobwebs and Quadream also invest in a company called I-OTT. I-OTT advertises itself as providing “combat training” for “guerrilla warfare” and consultations on “covert operations.” Its website states that I-OTT offers “customized intelligence solutions for governmental and private agencies” and claims to have offices in Israel, Mexico, and Brazil.
The 2017 version of its website stated they provide users with the basic effective “toolbox” for anti-terror and guerrilla warfare along with “training and consulting about covert operations and units.” Their software’s capabilities included generating “targeted research reports concerning almost any topic,” including “social unrest.” They also claimed to be operating “tailor-made avatars for collecting sensitive information.”
FALKOR
Quadream is connected to a company called Falkor, which specializes in mass data analysis. Falkor’s program combines open-source intelligence (OSINT) with social media intelligence (SOCMINT).
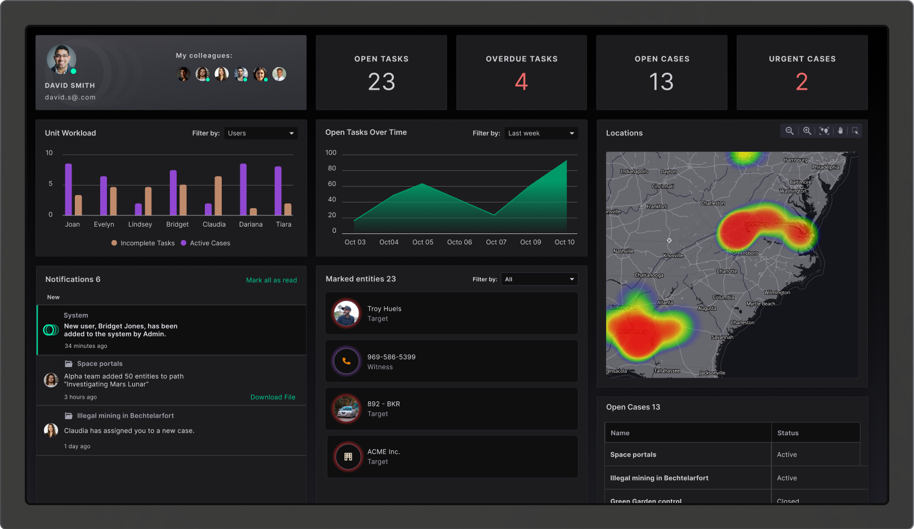
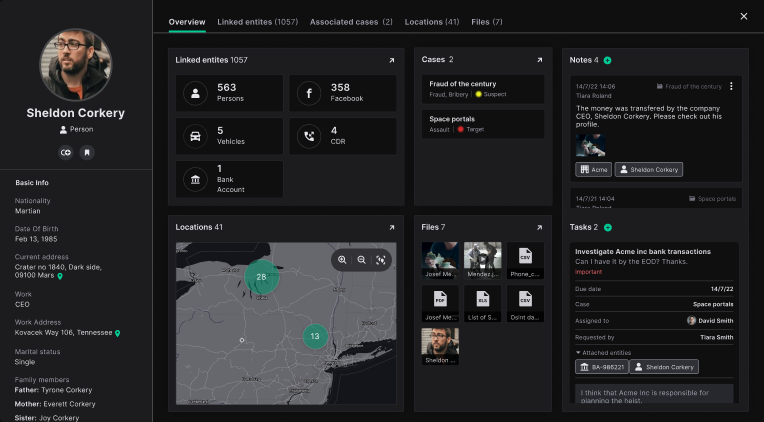
Amongst a plethora of things the programs do, they can create detailed connection charts. These charts display everyone in your life, including your boss, your second cousin, or anyone else you communicate with or have ever communicated with, including their contact information and heat maps showing where you or your associates travel. They also display bank accounts with bank account numbers.
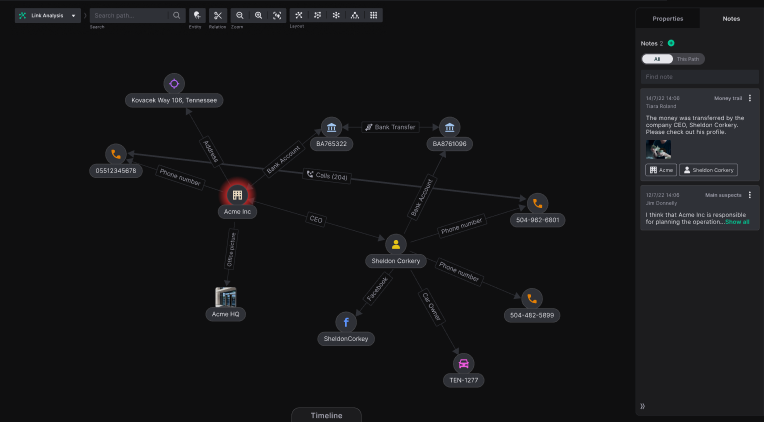
There are so many companies involved in this spy tech that I can’t possibly cover them all.
Uri Ashkenazi is an Israeli investor who not only has all of the aforementioned companies in his investment portfolio, but he is also the senior vice president of finance at Cobwebs. He is also the managing partner of Titan Ventures, a VC firm focused on Israeli cyber-intelligence investments, and a director of both I-OTT and Falkor Vision. Once again, everything is intertwined.
If what you have heard thus far doesn’t scare the absolute shit out of you, wait until you hear the next part….
NEXT READ: AD-BASED SURVEILLANCE [Flock Part 6]
Hey! Thanks for reading. The countdown is on, folks! Only a few more days until Truth Be Told: The Mega Event! Five of your favorite content creators will be giving a one-hour presentation on the topic of their choice. Come watch Unbekoming, David Parker, Jamie Andrews, Medicine Girl, and me put on a 6-hour show on September 17th! Get your ticket today. USE COUPON CODE "AGENT" AND GET $5 OFF!
If you can’t make the livestream, the replay will be available right after the show has ended.
Then, to make your fall delightful, grab a seat in my second class ever: The False Flag Masterclass! This six-week-long class is absolutely outstanding. I spent my entire summer making it because it is that important. Let me tell you about it because it is absolutely worth your time.
WEEK 1: The Rise of the False Flag Network will cover the very real network that spans across the world. In this first week I will cover exactly how it came to be, who is behind it, how it is funded, where specifically it operates, why these events occur, and more. This first class will be a dose of untold history in a way you have never seen it before. It will give you a lot of “ah-ha moments.”
WEEK 2: The Inner Workings of False Flags - Now that we have confirmed, beyond a shadow of a doubt, that there is a very real network, we can move on to addressing the elephant in the room: Who are these people that participate in this stuff? Where do they come from? Why do they partake in these events? What do they get out of it? Is everyone really in on it? We will also cover the CIA’s Psychological Warfare manual; what better way to get the facts than right from the source itself? This is a long class, nearly an hour and a half!
WEEK 3: How They Keep Them Quiet - The name of the class says it all. This is a very important question to answer because it is a huge key to the whole thing; how do they keep these people from talking? And the bigger question: Where are all the whistleblowers?
WEEK 4: Dissecting Two False Flags - It is not enough to learn what they are doing; we have to learn how they are doing it. This week we will dive deep into two tragedies in modern history, and I will show you everything wrong with them. You will be both alarmed and amazed at the tactics used to deceive us. For this week, I chose two events that you probably never considered examining, so it will be fresh material for pretty much everyone. You will learn a ton.
WEEK 5: The Biggest False Flag of Our Lifetimes? This week we will closely examine the inner workings of a recent, large-scale event that changed history in ways you have never been told. Spoiler Alert: Surprisingly, it actually isn’t 9/11.
WEEK 6: The Wrap-up - This is a long class, over an hour and a half again. In it, I will review everything we discussed and answer another very important question, “Just how deep does the fakery go?” When all’s said and done, you will look at the world with new eyes. Those of you who have researched these events over the years will have far deeper insight into the mechanics of them, and those of you who never considered that tragedies could be smoke and mirrors will sleep better at night knowing innocent people aren’t getting assassinated left and right. This course is incredibly valuable, not only to American citizens but also to people all over the world, because this isn’t happening just in the United States. If you want your eyes opened to truth, broadcast in a very easy way to understand--a way in which the material cannot be disputed--this is the ultimate class for you.
Best of all, this six-week class is only 25 dollars. Not 25 dollars per class, 25 dollars total. Grab your seat today. If you can’t make the livestreams, the replays will be available for you to watch anytime.
ENROLL NOW: The False Flag Masterclass
Be sure to subscribe so my articles get sent to your email!
Want to support my work? Buy Me a Coffee or Make a Ko-Fi Donation:
If you want to make sure you are updated when new articles, eBooks, events, and podcasts are released, be sure to sign up for WhatsApp notifications: